🚨 BOLO: Chrome Security Update: Law Firms Should Patch Before Browsing Again 🚨

lawyers keep your work secure, update your softwarE - update your google chrome browser now!

Solo practitioners and small firms should make updating Google Chrome a same-day task. Malwarebytes reports that Chrome’s current desktop update includes 327 security fixes, including 10 critical vulnerabilities, and that certain flaws can be triggered simply by visiting a malicious website. For a law practice handling confidential client communications, privileged work product, and sensitive financial data, that is a risk worth addressing immediately.

Chrome’s stable release has been updated to version 152.0.7977.64/.65 for Windows and Mac, and 152.0.7977.64 for Linux. The update addresses, among other issues, a critical flaw in ANGLE, Chrome’s graphics translation component, identified as CVE-2026-79282. Malwarebytes says a remote attacker could exploit that flaw through a crafted web page to execute arbitrary code outside Chrome’s browser sandbox.

That phrase—“outside the sandbox”—matters. Browser sandboxing is designed to contain web content so that a malicious site cannot easily reach the rest of the computer. A flaw that permits code execution beyond that boundary can give an attacker a path from a single web visit to the underlying operating system. That is precisely the sort of exposure lawyers should avoid when working in a browser alongside client portals, email, cloud document systems, court filing platforms, banking tools, and AI services. ⚖️

The update also remediates CVE-2026-78899, a use-after-free vulnerability in Chrome’s V8 JavaScript engine. It has a reported CVSS score of 8.8 out of 10. Even though successful exploitation occurs inside the browser sandbox, it should not be dismissed. Attackers frequently combine vulnerabilities in a chain, using one weakness to gain an initial foothold and another to widen access.

Why this is a legal-ethics issue!
its a team effort - remind your fellow lawyers to update their chrome browser today!

Technology hygiene is no longer separate from professional responsibility. ABA Model Rule 1.1 requires competent representation, and Comment 8 specifically calls on lawyers to keep abreast of “the benefits and risks associated with relevant technology.” A lawyer does not need to become a cybersecurity engineer. But maintaining a reasonably secure browser—the primary doorway to modern legal work—is a basic and manageable safeguard.

Model Rule 1.6(c) is equally relevant. It requires lawyers to make reasonable efforts to prevent unauthorized access to, or inadvertent disclosure of, client information. An unpatched browser can become an avoidable weak point in that effort. A compromised browser session could expose client documents, credentials, confidential messages, cloud-storage access, or data entered into web forms. 🔐

For firms, this update is also a reminder to think beyond the individual lawyer’s device. Rule 5.1 requires partners and managers to make reasonable efforts to ensure that firm-wide practices conform to professional obligations. Rule 5.3 similarly requires appropriate oversight of nonlawyer assistants. In practical terms, that means someone should own the checklist: browser updates, operating-system patches, password-manager deployment, multifactor authentication, and employee awareness.

Update Chrome now

On a Windows or Mac computer:

  1. Open Chrome.

  2. Select the three-dot More menu in the upper-right corner.

  3. Choose Settings.

  4. Select About Chrome.

  5. Allow Chrome to download any available update.

  6. Restart the browser to complete installation. 🔄
Chrome typically updates itself, but automatic updates can lag when the browser remains open for days, a restart is postponed, or an extension interferes with the update process. Malwarebytes specifically notes that manually checking can ensure the update is applied rather than merely downloaded.

This is a two-minute task with a potentially significant payoff. Before opening that unfamiliar link, reviewing a shared file, or logging into a client-facing platform, take a moment to confirm that Chrome is current. Security is not a one-time purchase or a single policy document. It is a set of small, repeatable habits that protect the practice and the people who trust it.

Bottom line: update Chrome, restart it, and encourage everyone in your firm to do the same today. ✅
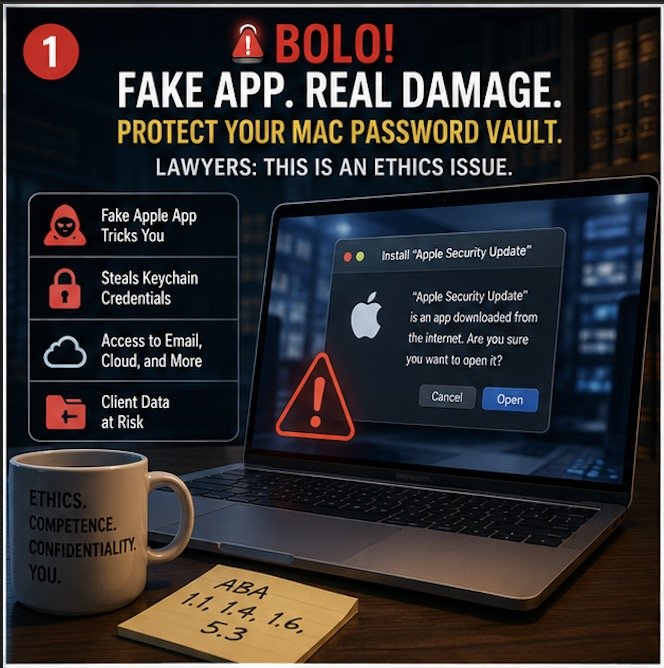
🚨BOLO! Fake Apple App Steals Mac Password Vaults: What Lawyers Must Do Now 🔐⚠️

If you use a Mac in your law practice, this is a “stop and read” moment.

Fake Apple App Threatens Lawyers’ Mac Password Security

A newly identified piece of malware—disguised as a legitimate Apple application—has the ability to trick users into surrendering access to their macOS password vault. That means saved credentials, system access, and potentially client data are all in play. For lawyers, the implications go well beyond inconvenience. This is an ethics issue. 🚨

According to Malwarebytes’ recent threat intelligence report, attackers are distributing a fake Apple app that convincingly mimics legitimate system prompts. Once installed, it requests elevated permissions and can capture macOS Keychain credentials—the same vault many attorneys rely on to store passwords and secure notes.

That should immediately raise a red flag for anyone responsible for client confidentiality.

Why This Matters for Lawyers

Many attorneys assume macOS provides a higher baseline of security. That assumption is not entirely wrong, but it is incomplete. Threat actors are increasingly targeting Mac users because of that very complacency.

If your Keychain is compromised, an attacker may gain access to:

  • Email accounts containing privileged communications 📧

  • Cloud storage platforms holding client files ☁️

  • Practice management systems

  • Financial accounts and trust systems 💼

This is not just a cybersecurity issue—it is a professional responsibility issue under multiple ABA Model Rules.

The Ethics Layer You Cannot Ignore

Let’s connect the dots to your obligations.

Mac Malware Mimics Apple Prompts to Steal Keychain Credentials

ABA Model Rule 1.6 (Confidentiality of Information) requires attorneys to make reasonable efforts to prevent unauthorized access to client information. Falling for a well-crafted phishing or malware attack does not automatically mean a violation—but failing to implement reasonable safeguards might.

ABA Model Rule 1.1 (Competence) now explicitly includes technological competence. Comment 8 makes clear that lawyers must understand the “benefits and risks associated with relevant technology.”

If you are not aware that fake system prompts exist—or that macOS Keychain can be targeted—you are already behind the curve.

ABA Model Rule 5.3 (Responsibilities Regarding Nonlawyer Assistance) also comes into play if your staff installs software or clicks prompts without proper training.

This is why I often emphasize in both my blog and podcast that cybersecurity is no longer optional—it is foundational.

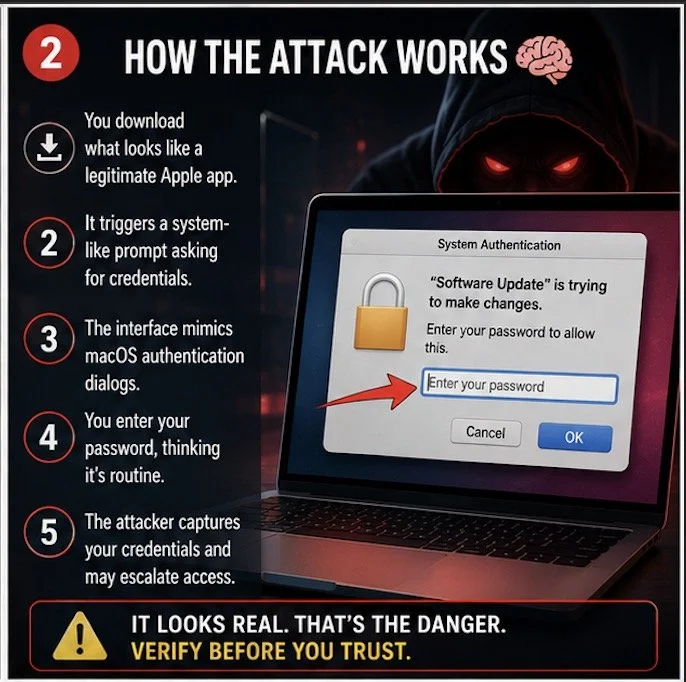
How the Attack Works 🧠

The attack is deceptively simple:

  • A user downloads what appears to be a legitimate Apple-related application.

  • The app triggers a system-like prompt requesting credentials.

  • The interface closely mimics macOS authentication dialogs.

  • The user enters their password, believing it is a routine request.

  • The attacker captures the credentials and may escalate access.

This is classic social engineering layered with technical sophistication.

And here is the uncomfortable truth: even experienced professionals can be fooled when the interface looks authentic.

Warning Signs You Should Not Ignore

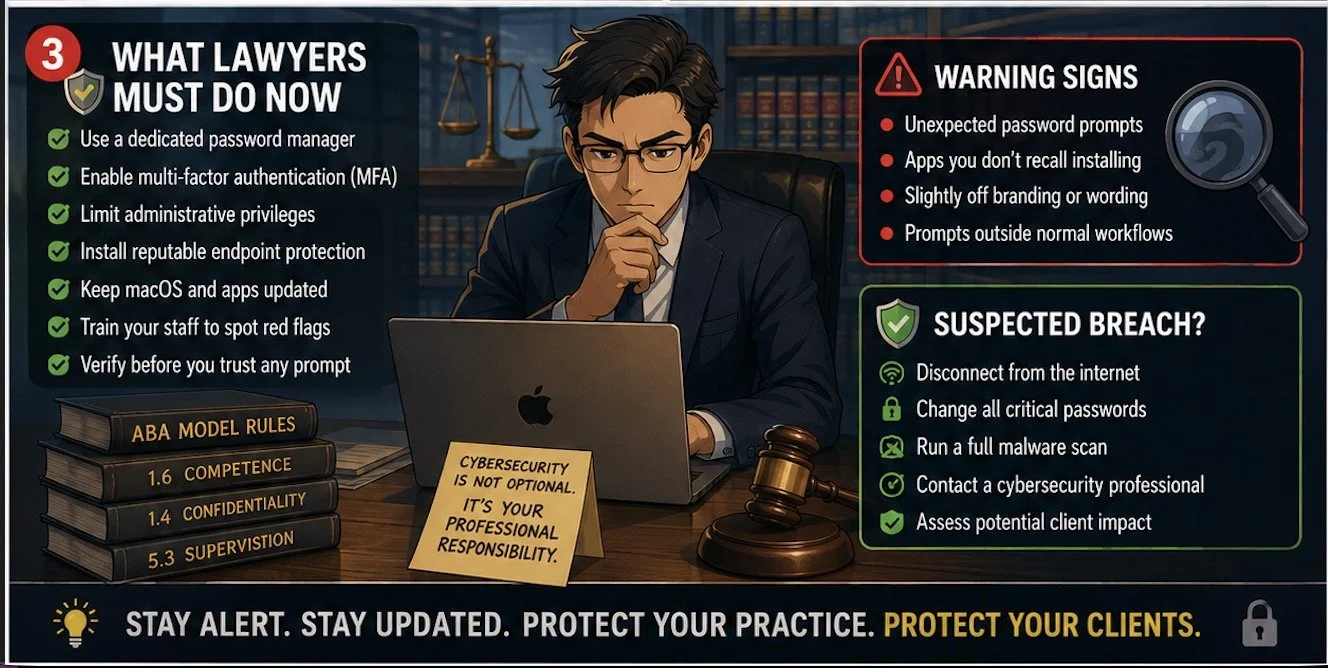
While these attacks are convincing, they are not perfect. Look for:

  • Unexpected prompts asking for your Mac password 🔑

  • Requests tied to apps you do not recall installing

  • Slightly off branding, spacing, or wording

  • Prompts appearing outside normal workflows

When in doubt, stop. Do not enter credentials.

Instead, open System Settings directly and verify whether any legitimate action requires authentication.

💡 TIP:  Download Apps directly from the Apple App Store.  These applications are vetted by Apple and are less likely to be malware!

Practical Safeguards for Your Practice 🛡️

You do not need to become a cybersecurity expert. But you do need a defensible baseline.

Start here:

  • Use a dedicated password manager instead of relying solely on Keychain.

  • Enable multi-factor authentication (MFA) across all critical systems.

  • Limit administrative privileges on your Mac.

  • Install reputable endpoint protection software.

  • Keep macOS and all applications updated.

  • Train your staff to recognize suspicious prompts.

Incident Response: What If You Already Clicked?

  • If you suspect you interacted with a fake app:

  • Disconnect from the internet immediately 🌐

  • Change all critical passwords from a separate, clean device

  • Run a full malware scan

  • Contact a cybersecurity professional

  • Assess whether client data may have been exposed

At that point, your ethical obligations may shift toward disclosure.

Under ABA Model Rule 1.4 (Communication), you may need to inform affected clients if their data was compromised. Timing and scope matter, so consult ethics counsel where appropriate.

Lawyers Must Strengthen Mac Cybersecurity and Client Data Protection

The Bigger Picture

This is not just about one fake app.

It is about a shift in the threat landscape. Attackers are no longer relying on obvious scams. They are leveraging trust—your trust in Apple, your trust in familiar interfaces, your trust in your own habits.

That is why vigilance must become part of your daily workflow.

As I have discussed before, technology amplifies both efficiency and exposure. The same tools that make your practice more productive also expand your attack surface.

Final Thought

You do not need to panic. But you do need to pay attention.

The lawyers who thrive in this environment are not the most technical—they are the most aware.

Stay alert. Stay updated. And treat every unexpected prompt like it matters—because it might. 🔍

BOLO: Microsoft Just Dropped Its Biggest Patch Tuesday Ever — Why Lawyers Must Update Windows Right Now! 🛡️

Lawyers should up their Windows products now — protect your client data from cyber threats!

If you are a lawyer and your Windows machine is sitting there, unpatched, you are not just leaving your front door unlocked — you are handing a master key to anyone who wants it. On June 10, 2026, Microsoft released what security researchers are calling the largest Patch Tuesday in the company's history — fixing 206 to 211* security vulnerabilities across WindowsOfficeSharePointExchangeDefenderBitLockerAzure, and more. That number is not a typo. The 12-month average for a typical Patch Tuesday hovers around 100 fixes. This month, Microsoft doubled it.

The Numbers That Should Get Your Attention 📊

Here is what landed in June 2026's update package:

  • 206–211* total vulnerabilities patched — the largest Patch Tuesday release ever recorded

  • 32–37* rated Critical — the most critical fixes in a single release, ever 54 Remote Code Execution (RCE) vulnerabilities — up from an average of ~26 per month 66 Elevation of Privilege vulnerabilities

  • 3 publicly disclosed zero-days — bad actors knew about these flaws before Microsoft patched them

  • 3 separate vulnerabilities rated CVSS 9.8 out of 10, all exploitable over the network with no user interaction required

Let those last four words sink in: no user interaction required. An attacker does not need you to click a phishing link or open a malicious attachment. They just need your machine to be reachable on a network — and your Windows installation to be unpatched.

The Vulnerabilities That Matter Most to Law Firms ⚠️

CVE-2026-47291 is a Critical RCE vulnerability in HTTP.sys rated CVSS 9.8, flagged "Exploitation More Likely," affecting all versions of Windows in mainstream support from Server 2016 through Windows 11. No privileges. No user interaction. Directly in the crosshairs: firms running web-facing client portals or remote desktop services. 🎯

CVE-2026-41091, affecting Microsoft Defender itself, is marked Exploitation Detected, Weaponized, and Publicly Aware . When your antivirus has a vulnerability that is already being actively weaponized in the wild, every hour you delay patching is an hour of unnecessary exposure.

CVE-2026-44815, a CVSS 9.8 RCE in the DHCP Client Service, and CVE-2026-50508, a Windows NTLM Spoofing vulnerability flagged "Exploitation More Likely," round out the priority list for law firms using Windows domain authentication.

The Secure Boot Factor: A Slower-Moving Risk 🔐

lawyers update your Windows security shield to block zero-day attacks on law firms!

Separate from the Patch Tuesday rush, June 2026 marks an important Secure Boot certificate transition. The certificates shipped inside Windows since 2011 are being replaced with new 2023-dated certificates valid until 2038. Microsoft is rolling these out through normal Windows Update, but some older devices need a BIOS firmware update from the manufacturer before the transition can complete. If your firm runs machines built before 2024, open Windows Security → Device Security → Secure Boot and verify the status text — not just the color. Microsoft warns that a green checkmark alone does not confirm the new certificates have been applied.

🚨This Is an Ethics Issue. Full Stop. ⚖️

ABA Model Rule 1.1 requires competent representation, and Comment 8 explicitly extends that duty to include "the benefits and risks associated with relevant technology”.  Staying abreast of a historic, record-breaking security release is not optional — it is the standard. ABA Model Rule 1.6 requires lawyers to make "reasonable efforts to prevent the inadvertent or unauthorized disclosure of, or unauthorized access to, information relating to the representation of a client". Running unpatched software on machines holding client files is almost certainly not "reasonable." Formal ethics opinions across multiple jurisdictions have made clear that annual technology assessment, patching, and investing in updated software versions are baseline expectations. ABA Model Rule 5.3 places the supervision obligation squarely on the supervising attorney — if you manage a firm and your IT vendor has not deployed these patches, that exposure lands on you.

The ABA now considers "reasonable cybersecurity" an ethical requirement under Rule 1.6. A record-breaking, 200+ vulnerability patch release is exactly the kind of event the ABA had in mind.

How to Update Right Now (Three Minutes or Less) ⏱️

You do not need IT for this:

be a Tech-savvy lawyer and secure your law firm’s networks with timely updates!

✅ Click Start → Settings (gear icon)

✅ Select Windows Update

✅ Click Check for Updates

✅ Download and install everything that appears

✅ Click Restart now when prompted

✅ Return to Windows Update and verify "You're up to date"

If you manage other attorneys or staff, send this post to them right now. Contact your IT vendor today and request written confirmation that June 2026 Patch Tuesday updates have been deployed across all firm devices.

The Bottom Line 🔑

This is the biggest patch release in Microsoft's history. It includes actively exploited vulnerabilities, three CVSS 9.8 flaws requiring no user interaction, and a Defender vulnerability already in the wild. For solo practitioners and small firms — statistically among the most targeted and least-defended organizations in the legal sector — this update is not background noise. It is a call to action. Be tech-savvy. Protect your clients. Protect your license. Update your machines. 💪

BOLO: Gone (Almost) Phishin’: What a Sophisticated Apple Scam Teaches Lawyers About Cybersecurity, Client Confidentiality, and ABA Ethical Duties 🚨📱

Lawyers Face Sophisticated Apple Phishing Scam Cybersecurity Risks!

A recent real‑world phishing attempt against a well‑known technology CEO offers an important warning for lawyers and law firms about how modern scams now convincingly mimic “legitimate” security workflows. This attack did not rely on laughable grammar, obvious fake domains, or clumsy social engineering; instead, it weaponized Apple’s genuine password‑reset system, real support case IDs, and realistic phone support to try to compromise the victim’s Apple ID. For lawyers who increasingly rely on mobile devices, cloud services, and multi‑factor authentication for client communications, this kind of scam is not hypothetical—it's a direct threat to client confidentiality and professional responsibility.

In the incident, the victim’s Apple Watch, iPhone, and Mac all began displaying unexpected prompts to reset the Apple ID password, despite the user running Apple’s Lockdown Mode on all devices. The prompts were not generated by malware on the devices, but by an attacker repeatedly triggering Apple’s legitimate password reset flow, thereby flooding the user with authentic-looking notifications. From the perspective of a busy lawyer, such prompts might be dismissed as an annoyance or, worse, acted upon in haste. Either reaction, without careful verification, can create risk. 📲

The scam escalated when the attacker called, posing as “Alexander from Apple Support,” referencing a real Apple support case that they had opened themselves by impersonating the victim. Because Apple’s own systems generated a valid case ID and corresponding emails, the communications appeared fully authentic; no spam filter or “phishing awareness” toolbar would have flagged them as suspicious. The caller began with correct, even prudent, security advice—check your account, verify nothing has changed, consider updating your password—which is precisely the kind of guidance many lawyers expect from legitimate support channels. This blend of real security language with a fraudulent goal is what makes the scam so dangerous. 🧠

Phishing Lessons for Lawyers Using Apple Devices and Cloud Tools!

The critical moment came when “Alexander” sent a text with a link to “audit-apple.com,” a pixel‑perfect imitation of Apple’s site that displayed the real case ID and even a fake transcript of the attackers’ prior “chat” with Apple. At the bottom of the page sat a “Sign in with Apple” button, intended to harvest the victim’s credentials under the guise of closing a fraudulent request. Only after poking at the site and noticing that any case ID produced the same result did the victim confirm it was a scam and confront the attacker. Many lawyers, particularly those with only moderate comfort with technology, might not test the site this way and could be persuaded by the case ID and realistic presentation. 🕵️‍♂️

For legal professionals, the ethical implications are significant. ABA Model Rule 1.1 on competence requires lawyers to understand the benefits and risks associated with relevant technology, including the ability to recognize and respond to sophisticated phishing. The duty of confidentiality under Rule 1.6 requires taking reasonable steps to prevent unauthorized access to client information, which includes protecting accounts and devices that store or access client files, email, and messaging. If a lawyer’s Apple ID or similar account is compromised, attackers may gain access to privileged communications, document repositories, calendar entries, and even secure messaging apps that sync via the device.

Model Rule 5.3 extends these obligations to nonlawyer assistants, including staff and outside vendors who may handle client data or access firm systems. If partners and associates are vulnerable to such scams, staff and contractors are as well; firm leadership must implement policies, training, and incident‑response procedures that recognize the new generation of phishing where everything “looks right” until you inspect the URL or underlying flow. This aligns with recognized best practices: anti‑phishing training, simulated phishing exercises, and clear escalation paths for suspicious security communications.

Key practical lessons for lawyers from this incident include:

  • Do not approve unexpected password‑reset prompts; instead, go directly to your device or account settings via a known‑good path (e.g., Settings → Apple ID on your device).

  • Treat unsolicited “support” calls with extreme skepticism, even when they reference real case IDs or recent activity; major vendors like Apple will not call you out of the blue to fix a security issue.

  • Always verify the URL before entering credentials; for Apple, support should live on apple.com or getsupport.apple.com, not look‑alike domains.

  • Establish a firm‑wide rule: no one—IT, vendors, or support—will ever ask for passwords, one‑time codes, or sign‑in via a link sent in an unsolicited message; any such request must be verified through a separate, trusted channel.

Apple Scam Warning for Lawyers Protecting Client Confidentiality

From an ethical‑risk perspective, a successful attack of this kind could trigger duties to notify clients, insurers, and regulators, depending on your jurisdiction’s breach‑notification regime and professional‑conduct rules. Even an “almost‑breach,” like the one described in this article, is a valuable opportunity for firms to revisit incident‑response plans, document what would happen if a lawyer’s Apple ID or smartphone were compromised, and rehearse the steps for containing damage. Doing so not only supports compliance with Model Rules 1.1 and 1.6 but also demonstrates to clients and courts that the firm takes cybersecurity governance seriously. ✅

The story also underscores that even highly technical users can be momentarily convinced by a well‑crafted scam, which should encourage humility rather than embarrassment among lawyers who worry they are “not technical enough.” The correct response is not shame, but systems: layered security controls, clear verification procedures, and regular training that turn individual vigilance into institutional resilience. Ultimately, as phishing attacks become more sophisticated and exploit real security workflows, lawyers must elevate their cybersecurity awareness to meet their ethical obligations and preserve the trust at the core of the attorney‑client relationship. 💼

🚨BOLO: Last-Minute Procurement Scams Targeting Firms on Christmas Eve🎄

It is Christmas Eve! The pressure to secure last-minute client gifts, finalize year-end office supply orders, or purchase personal items is at its peak. Scammers anticipate this desperation. They are currently flooding social media and search engines with "Out-of-Stock" Purchase Scams designed to exploit your urgency.

Whether you are ordering toner for year-end filings or a rush gift for a partner, the mechanism remains the same. You locate a vendor promising immediate delivery of a hard-to-find item. You purchase it. Minutes later, an email arrives claiming the item is "out of stock" due to holiday volume.

This notification is the trap. It promises an instant refund but requires you to click a link to "confirm" your details. This link does not lead to a payment processor; it leads to a credential-harvesting site. By trying to recoup your funds, you may inadvertently hand over firm credit card data or banking login credentials to a threat actor.

Immediate Risk Mitigation:

  • Verify the Vendor: If a deal appears for an item sold out everywhere else, it is likely a lure. Stick to established, major retailers today.

  • Isolate Transactions: Do not mix firm procurement with personal panic buying. Use a dedicated credit card for any new vendor.

  • Pause Before Clicking: If you receive a refund link, do not click it. Legitimate refunds happen automatically; they never require you to log in again.

Stay safe. Do not let a shipping deadline become a security breach. 🎄🔒

🚨 BOLO: Samsung Budget Phones Contain Pre-Installed Data-Harvesting Software: Critical Action Steps for Legal Professionals

‼️ ALERT: Hidden Spyware in Samsung Phones!

Samsung Galaxy A, M, and F series smartphones contain pre-installed software called AppCloud, developed by ironSource (now owned by Unity Technologies), that harvests user data, including location information, app usage patterns, IP addresses, and potentially biometric data. This software cannot be fully uninstalled without voiding your device warranty, and it operates without accessible privacy policies or explicit consent mechanisms. Legal professionals using these devices face significant risks to attorney-client privilege and confidential client information.

The Threat Landscape

AppCloud runs quietly in the background with permissions to access network connections, download files without notification, and prevent phones from sleeping. The application is deeply integrated into Samsung's One UI operating system, making it impossible to fully remove through standard methods. Users across West Asia, North Africa, Europe, and South Asia report that even after disabling the application, it reappears following system updates.

The digital rights organization SMEX documented that AppCloud's privacy policy is not accessible online, and the application does not present users with consent screens or terms of service disclosures. This lack of transparency raises serious ethical and legal compliance concerns, particularly for attorneys bound by professional responsibility rules regarding client confidentiality.

Legal and Ethical Implications for Attorneys

Under ABA Model Rule 1.6, attorneys must make "reasonable efforts to prevent the inadvertent or unauthorized disclosure of, or unauthorized access to, information relating to the representation of a client". The duty of technological competence under Rule 1.1, Comment 8, requires attorneys to "keep abreast of changes in the law and its practice, including the benefits and risks associated with relevant technology".

The New York Bar's 2022 ethics opinion specifically addresses smartphone security, prohibiting attorneys from sharing contact information with smartphone applications unless they can confirm that no person will view confidential client information and that data will not be transferred to third parties without client consent. AppCloud's data harvesting practices appear to violate both conditions.

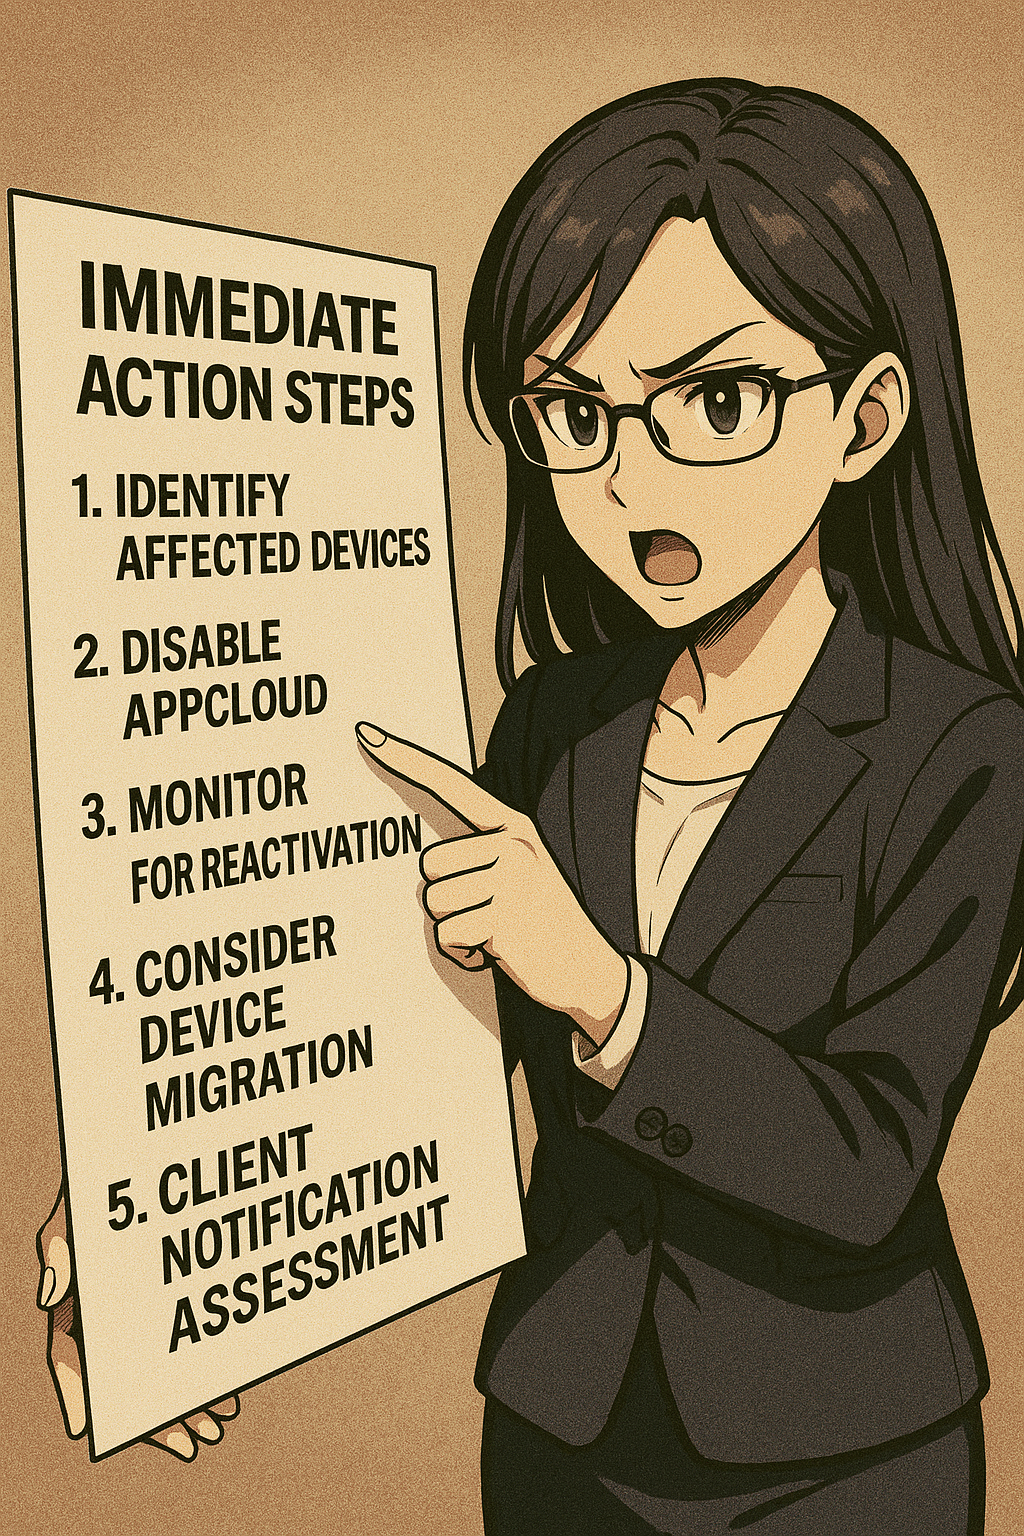
Immediate Action Steps

‼️ Act now if you’ve purchased certain samsung phones - your bar license could be in jeopardy!

Step 1: Identify Affected Devices
Check whether you use a Samsung Galaxy A series (A05 through A56), M series (M01 through M56), or F series device. These budget and mid-range models are primary targets for AppCloud installation.

Step 2: Disable AppCloud
Navigate to Settings > Apps > Show System Apps > AppCloud > Disable. Additionally, revoke notification permissions, restrict background data usage, and disable the "Install unknown apps" permission.

Step 3: Monitor for Reactivation
After system updates, return to AppCloud settings and re-disable the application.

Step 4: Consider Device Migration
For attorneys handling highly sensitive matters, consider transitioning to devices without pre-installed data collection software. Document your decision-making process as evidence of reasonable security measures.

Step 5: Client Notification Assessment
Evaluate whether client notification is required under your jurisdiction's professional responsibility rules. California's Formal Opinion 2020-203 addresses obligations following an electronic data compromise.

The Bottom Line

Budget smartphone economics should not compromise attorney-client privilege. Samsung's partnership with ironSource places aggressive advertising technology on devices used by legal professionals worldwide. Until Samsung provides transparent opt-out mechanisms or removes AppCloud entirely, attorneys using affected devices should implement immediate mitigation measures and document their security protocols.

🚨 BOLO: Widespread Internet Disruption from Cloudflare Infrastructure Failure

⚠️ legal professionals need to know how to adjust when the internet’s infrastructure goes down!

On November 18, 2025, at 11:20 UTC, Cloudflare experienced a significant network outage that disrupted critical internet services relied upon by millions globally, including legal professionals and their practice management tools. The incident lasted approximately six hours before full resolution at 17:06 UTC.

The outage originated from a latent bug within Cloudflare's Bot Management configuration file. During a routine configuration update, the file size exceeded anticipated parameters, causing the bot detection module to fail and triggering cascading HTTP 500 errors across the network. The root cause was neither a cyberattack nor malicious activity, but rather a software defect in the core proxy system that processes all traffic transiting Cloudflare's infrastructure.

Impact on Legal Professionals: Law firms utilizing cloud-based practice management systems, document automation platforms, and client communication portals may have experienced access disruptions. Websites hosting legal resources, contract repositories, and time-tracking applications served through Cloudflare may have been unavailable. Authentication systems, including Cloudflare Access—commonly deployed for secure remote work environments—failed broadly during the incident.

Critical Irony: Downdetector, the primary outage-monitoring platform relied upon by IT professionals to confirm infrastructure problems, was itself offline during the incident due to Cloudflare dependency.

Operational Lessons: This event underscores the concentration risk inherent in modern internet infrastructure. Legal practices should evaluate redundancy protocols, maintain documented failover procedures, and ensure business continuity plans account for third-party provider dependencies that exist outside their direct control.

👨‍⚖️ Ethical Obligations: Under ABA Model Rules 1.1 (technological competence), 1.6 (confidentiality), and 5.3 (third-party vendor supervision), lawyers must document both incidents' impact on client matters and reassess business continuity protocols.

Action Items: Review your practice's infrastructure vendor relationships and assess SLA terms for meaningful uptime guarantees and compensation mechanisms.

🚨BOLO: Critical Samsung Zero-Day Alert: CVE-2025-21042 Enables Device Takeover via Malicious Images

Federal government warns of spyware aimed at some samsung galaxy devices - update your software now!!!

Samsung Galaxy devices face critical exploitation through CVE-2025-21042, a zero-day vulnerability enabling complete device takeover. CISA added this flaw to its Known Exploited Vulnerabilities catalog on November 10, 2025. Threat actors deployed LANDFALL spyware via malicious DNG image files sent through WhatsApp, requiring zero user interaction. This out-of-bounds write vulnerability in Samsung's image processing library allows remote code execution, data theft, and surveillance. Affected models include Galaxy S22, S23, S24 series, Z Fold4, and Z Flip4. Samsung patched this April 2025, but exploitation occurred for months prior. Federal agencies must remediate by December 1, 2025.

‼️Action Required‼️: Update devices immediately and scrutinize unsolicited image files!

🎙️ TSL Labs! Google AI Discussion of MTC: 🚨‼️ Emergency BOLO! 🚨‼️ Lawyers on the Go: Essential Tech Strategies for Air Travel During the Government Shutdown ✈️

📌 Too Busy to Read This Week's Editorial?

Join us for an emergency professional deep dive into essential tech strategies for air travel during government shutdowns and travel disruptions. 🛫 This AI-powered roundtable unpacks Michael D.J. Eisenberg's critical editorial with actionable intelligence on real-time flight tracking, data security protocols, connectivity redundancy, and power management. Whether you're a legal professional navigating travel chaos or anyone managing disruptions during system-wide stress, discover how to transform from reactive scrambling to proactive control—turning travel crises into manageable projects you command. Learn the five professional-grade rules that separate those who navigate disruptions from those who get derailed.

In our conversation, we cover the following:

  • 00:00:00 – Introduction: Welcome to Tech Savvy Lawyer Labs Emergency BOLO

  • 00:01:00 – Travel Chaos as the New Normal: System Volatility & Professional Vulnerability

  • 00:02:00 – Flight Schedule Control: The Illusion & Reality of Travel Disruptions

  • 00:02:00 – Extreme Volatility in Air Travel: Cascading Flight Cancellations & Customer Service Chaos

  • 00:02:00 – Real-Time Flight Tracking Strategy: Flightradar24 & FlightAware Intelligence Systems

  • 00:02:00 – Backup Flight Monitoring: Multi-Carrier Surveillance Strategy (Delta, United, American)

  • 00:03:00 – Proactive Intelligence vs. Reactive Response: One-Hour Lead Time Advantage

  • 00:03:00 – Early Rebooking Strategy: First and Second Choice Flight Selection

  • 00:03:00 – Trusted Traveler Programs: TSA PreCheck & Time Investment ROI

  • 00:03:00 – TSA PreCheck Value: $78 for Five Years & Security Line Efficiency

  • 00:03:00 – Global Entry: $100 for Five Years with International Customs Acceleration

  • 00:04:00 – Trusted Traveler Planning: Background Checks, Interviews & Months-Ahead Application

  • 00:04:00 – Public WiFi Malpractice Alert: Data Security & Vulnerability Assessment

  • 00:04:00 – Personal Mobile Hotspot: Cellular Encryption Over Public Networks

  • 00:05:00 – Dual Carrier Coverage: eSIM Technology & Connectivity Insurance

  • 00:05:00 – Dual SIM Implementation: T-Mobile & Verizon Redundancy Strategy Without Two Phones

  • 00:05:00 – eSIM Digital Technology: Two Active Lines on One Device

  • 00:05:00 – Prepaid Data Plan Strategy: Coffee-Price Monthly Cost for Connectivity Backup

  • 00:06:00 – VPN Non-Negotiables: Encrypted Tunnel & Automatic Connection Protocol

  • 00:06:00 – VPN Automatic Startup: Device Initialization & All-Device Coverage (Phone, Tablet, Laptop)

  • 00:06:00 – International Travel Security: VPN Encryption & Surveillance Protection

  • 00:07:00 – TSA-Approved Power Banks: 100 Watt-Hour Specifications & 27,000 mAh Ceiling

  • 00:07:00 – Laptop Charging: 100-Watt USB-C Power Bank Requirements (MacBook Pro)

  • 00:07:00 – Multi-Device Charging: Simultaneous Laptop, Phone & Tablet Power Delivery

  • 00:07:00 – Smart Power Display: Charging Speed Monitoring & Juice Rationing

  • 00:07:00 – Surge Protector Safety: Airport Outlet Protection & Device Insurance

  • 00:08:00 – Airport Lounges: Priority Pass Access & Productivity Sanctuaries (1,300+ Worldwide)

  • 00:08:00 – Travel Credit Card Benefits: Complimentary Lounge Visits Strategy

  • 00:08:00 – Conference Call Chaos: Professional Communication Environment Solutions

  • 00:08:00 – Noise-Canceling Headphones: Sony XM5 & Bose QuietComfort Professional Focus

  • 00:08:00 – Battery Life Requirements: 30-40 Hour Endurance for Extended Delays

  • 00:09:00 – Offline Access Mandate: Pre-Departure Critical File Downloads

  • 00:09:00 – Six-Hour Offline Capability: Zero-Connectivity Work Strategy

  • 00:09:00 – Adobe Scan App: OCR Technology & Mobile Document Management

  • 00:10:00 – Adobe Ecosystem Syncing: Cross-Device Workflow & E-Signature Integration

  • 00:10:00 – Apple Ecosystem Continuity: iPhone, iPad & MacBook Seamless Integration

  • 00:10:00 – FileVault Encryption & Face ID: Built-In Security Non-Negotiables

  • 00:11:00 – Five Professional-Grade Rules: Pre-Travel Checklist & Crisis Preparation

  • 00:11:00 – Rule One: Full Device Charge Before Departure

  • 00:11:00 – Rule Two: Offline Maps & Critical Files Downloaded Locally

  • 00:11:00 – Rule Three: Screenshot Everything (Boarding Passes, Hotel, Car Rental)

  • 00:11:00 – Rule Four: Distributed Charger Storage Across Multiple Bags for Backup Power

  • 00:11:00 – Rule Five: Share Itinerary with Emergency Contact

  • 00:11:00 – Post-Crisis Integration: Permanent Daily Workflow Implementation

  • 00:11:00 – The Bigger Question: Crisis Tools as Permanent Professional Standards

  • 00:12:00 – Transition to AI Ethics Discussion: Hidden AI Crisis in Legal Practice Teaser

  • 00:14:00 – Conclusion: Tech Savvy Lawyer Labs Roundtable Summary & Resources

Resources 📚

Mentioned in the episode:

Hardware mentioned in the conversation:

Software & Cloud Services mentioned in the conversation: